
#tor
tor
10,612 views
21 Discussing
Hot
Latest

·
--
Bitcoin Core discloses Tor privacy vulnerability! Thousands of nodes once mistakenly trusted unknown connections
The Bitcoin network has long been known for its decentralization and security, but its underlying software is not without vulnerabilities.
On November 10, Bitcoin Core publicly disclosed a security vulnerability involving connections to the Tor network, identified as CVE-2025-62860.
Simply put, some nodes were configured with whitelists that granted higher privileges only to specific trusted connections. But due to an issue with the software’s detection mechanism, unknown users connecting through Tor could also be mistakenly treated as trusted connections.
Bitcoin Core disclosed that, under certain configurations, thousands of reachable mainnet nodes had once whitelisted all incoming Tor connections. As a result, some restrictions on spam traffic and privacy protection mechanisms could be bypassed.
First, not all Bitcoin nodes were affected. Only nodes with a specific non-default whitelist configuration enabled, and whose Tor proxy addresses fell within the corresponding range, were at risk.
Second, the vulnerability has already been fixed. Bitcoin Core addressed the issue in versions 30.0, 29.2, and 28.3, released in October 2025. This disclosure simply makes the technical details public.
The disclosure also accompanied two other security vulnerabilities. One could, under certain circumstances, prevent miner nodes from generating block templates correctly, while another could allow malicious connections to delay a node’s processing of new blocks.
It is worth noting that the publicly available information does not show that these vulnerabilities were ever exploited in practice.
In my view, what truly matters about this incident is not causing alarm, but reminding everyone that the security of the Bitcoin network depends not only on its consensus mechanism, but also on the software maintenance and configuration management of every node.
Decentralization does not mean that vulnerabilities will never exist. Timely upgrades and public scrutiny are essential to the network’s long-term security.
#BTC #Tor #比特币core披露tor流量漏洞
Bitcoin Core discloses Tor privacy vulnerability! Thousands of nodes once mistakenly trusted unknown connections
The Bitcoin network has long been known for its decentralization and security, but its underlying software is not without vulnerabilities.
On November 10, Bitcoin Core publicly disclosed a security vulnerability involving connections to the Tor network, identified as CVE-2025-62860.
Simply put, some nodes were configured with whitelists that granted higher privileges only to specific trusted connections. But due to an issue with the software’s detection mechanism, unknown users connecting through Tor could also be mistakenly treated as trusted connections.
Bitcoin Core disclosed that, under certain configurations, thousands of reachable mainnet nodes had once whitelisted all incoming Tor connections. As a result, some restrictions on spam traffic and privacy protection mechanisms could be bypassed.
First, not all Bitcoin nodes were affected. Only nodes with a specific non-default whitelist configuration enabled, and whose Tor proxy addresses fell within the corresponding range, were at risk.
Second, the vulnerability has already been fixed. Bitcoin Core addressed the issue in versions 30.0, 29.2, and 28.3, released in October 2025. This disclosure simply makes the technical details public.
The disclosure also accompanied two other security vulnerabilities. One could, under certain circumstances, prevent miner nodes from generating block templates correctly, while another could allow malicious connections to delay a node’s processing of new blocks.
It is worth noting that the publicly available information does not show that these vulnerabilities were ever exploited in practice.
In my view, what truly matters about this incident is not causing alarm, but reminding everyone that the security of the Bitcoin network depends not only on its consensus mechanism, but also on the software maintenance and configuration management of every node.
Decentralization does not mean that vulnerabilities will never exist. Timely upgrades and public scrutiny are essential to the network’s long-term security.
#BTC #Tor #比特币core披露tor流量漏洞
The Bitcoin network has long been known for its decentralization and security, but its underlying software is not without vulnerabilities.
On November 10, Bitcoin Core publicly disclosed a security vulnerability involving connections to the Tor network, identified as CVE-2025-62860.
Simply put, some nodes were configured with whitelists that granted higher privileges only to specific trusted connections. But due to an issue with the software’s detection mechanism, unknown users connecting through Tor could also be mistakenly treated as trusted connections.
Bitcoin Core disclosed that, under certain configurations, thousands of reachable mainnet nodes had once whitelisted all incoming Tor connections. As a result, some restrictions on spam traffic and privacy protection mechanisms could be bypassed.
First, not all Bitcoin nodes were affected. Only nodes with a specific non-default whitelist configuration enabled, and whose Tor proxy addresses fell within the corresponding range, were at risk.
Second, the vulnerability has already been fixed. Bitcoin Core addressed the issue in versions 30.0, 29.2, and 28.3, released in October 2025. This disclosure simply makes the technical details public.
The disclosure also accompanied two other security vulnerabilities. One could, under certain circumstances, prevent miner nodes from generating block templates correctly, while another could allow malicious connections to delay a node’s processing of new blocks.
It is worth noting that the publicly available information does not show that these vulnerabilities were ever exploited in practice.
In my view, what truly matters about this incident is not causing alarm, but reminding everyone that the security of the Bitcoin network depends not only on its consensus mechanism, but also on the software maintenance and configuration management of every node.
Decentralization does not mean that vulnerabilities will never exist. Timely upgrades and public scrutiny are essential to the network’s long-term security.
#BTC #Tor #比特币core披露tor流量漏洞
1
1.5k
·
--
#BitcoinCoreDisclosesTorTrafficVulnerability Don’t panic over the Tor bug news. The real story is “delay,” not “danger.” 🧅
Bitcoin Core disclosed 3 patched vulnerabilities. “Thousands” of reachable mainnet nodes were whitelisting incoming Tor connections, which removed some DoS limits and privacy protections. Nodes that didn’t have this non-default setting were not affected. (theblock)
The truth about the timeline:
✅ The fix was included in Bitcoin Core 30.0 (Oct 10, 2025) and 29.2 (Oct 14, 2025). The last vulnerable version reached end-of-life on Oct 27, 2026.
✅ The project ships the fix first, then shares the vulnerability details later.
⚠️ This is not an issue with consensus rules. The risk was to node privacy and reliability, not to coins or the Bitcoin protocol. (theblock) (cryptovalleyjournal)
My analysis: This is a textbook example of “responsible disclosure.” First the patch, then time for users to upgrade, and only then a public advisory. That’s the power of open source: a bug is found, fixed, and later everything is made public. But there’s a lesson here too: operators running old node versions should upgrade now.
(Not financial advice, DYOR.)
Do you run your own node, or do you trust an exchange/custodian? Why? 👇
#BitcoinCoreDisclosesTorTrafficVulnerability #Bitcoin❗ #Tor #BitcoinCore
#BitcoinCoreDisclosesTorTrafficVulnerability Don’t panic over the Tor bug news. The real story is “delay,” not “danger.” 🧅
Bitcoin Core disclosed 3 patched vulnerabilities. “Thousands” of reachable mainnet nodes were whitelisting incoming Tor connections, which removed some DoS limits and privacy protections. Nodes that didn’t have this non-default setting were not affected. (theblock)
The truth about the timeline:
✅ The fix was included in Bitcoin Core 30.0 (Oct 10, 2025) and 29.2 (Oct 14, 2025). The last vulnerable version reached end-of-life on Oct 27, 2026.
✅ The project ships the fix first, then shares the vulnerability details later.
⚠️ This is not an issue with consensus rules. The risk was to node privacy and reliability, not to coins or the Bitcoin protocol. (theblock) (cryptovalleyjournal)
My analysis: This is a textbook example of “responsible disclosure.” First the patch, then time for users to upgrade, and only then a public advisory. That’s the power of open source: a bug is found, fixed, and later everything is made public. But there’s a lesson here too: operators running old node versions should upgrade now.
(Not financial advice, DYOR.)
Do you run your own node, or do you trust an exchange/custodian? Why? 👇
#BitcoinCoreDisclosesTorTrafficVulnerability #Bitcoin❗ #Tor #BitcoinCore
Bitcoin Core disclosed 3 patched vulnerabilities. “Thousands” of reachable mainnet nodes were whitelisting incoming Tor connections, which removed some DoS limits and privacy protections. Nodes that didn’t have this non-default setting were not affected. (theblock)
The truth about the timeline:
✅ The fix was included in Bitcoin Core 30.0 (Oct 10, 2025) and 29.2 (Oct 14, 2025). The last vulnerable version reached end-of-life on Oct 27, 2026.
✅ The project ships the fix first, then shares the vulnerability details later.
⚠️ This is not an issue with consensus rules. The risk was to node privacy and reliability, not to coins or the Bitcoin protocol. (theblock) (cryptovalleyjournal)
My analysis: This is a textbook example of “responsible disclosure.” First the patch, then time for users to upgrade, and only then a public advisory. That’s the power of open source: a bug is found, fixed, and later everything is made public. But there’s a lesson here too: operators running old node versions should upgrade now.
(Not financial advice, DYOR.)
Do you run your own node, or do you trust an exchange/custodian? Why? 👇
#BitcoinCoreDisclosesTorTrafficVulnerability #Bitcoin❗ #Tor #BitcoinCore
9

·
--
Over the past few days, I’ve visited several onion web marketplaces because I was curious about the coins used for buying and selling there. I found some legendary coins used on those onion markets: $BTC , $LTC , $XMR . It turns out that privacy coins aren’t the only ones used there; transparent coins like BTC are also very popular. Of course, I was only looking at what was being sold on the onion web, and I don’t recommend visiting those sites either. I advise against making transactions on markets like these, as those websites could be traps set by Interpol or the FBI. That’s all, thank you.
#onion
#Privacy
#DarkWebRisk
#Tor
Over the past few days, I’ve visited several onion web marketplaces because I was curious about the coins used for buying and selling there. I found some legendary coins used on those onion markets: $BTC , $LTC , $XMR . It turns out that privacy coins aren’t the only ones used there; transparent coins like BTC are also very popular. Of course, I was only looking at what was being sold on the onion web, and I don’t recommend visiting those sites either. I advise against making transactions on markets like these, as those websites could be traps set by Interpol or the FBI. That’s all, thank you.
#onion
#Privacy
#DarkWebRisk
#Tor
#onion
#Privacy
#DarkWebRisk
#Tor
197

·
--
Tor‑enabled BTCPay is about to get a privacy upgrade.
Docker users will need to actively opt‑in to Tor on their next update, or they’ll lose onion‑only access. Existing Tor data stays intact, but the switch isn’t automatic.
This extra step highlights the growing emphasis on censorship‑resistant payment routes in crypto commerce. It also reminds operators that privacy isn’t set‑and‑forget—it requires ongoing attention.
💬 How will you handle the opt‑in process for your BTCPay deployment? BTCPay Tor CryptoPrivacy
#BTCPay #Tor #CryptoPrivacy
Tor‑enabled BTCPay is about to get a privacy upgrade.
Docker users will need to actively opt‑in to Tor on their next update, or they’ll lose onion‑only access. Existing Tor data stays intact, but the switch isn’t automatic.
This extra step highlights the growing emphasis on censorship‑resistant payment routes in crypto commerce. It also reminds operators that privacy isn’t set‑and‑forget—it requires ongoing attention.
💬 How will you handle the opt‑in process for your BTCPay deployment? BTCPay Tor CryptoPrivacy
#BTCPay #Tor #CryptoPrivacy
Docker users will need to actively opt‑in to Tor on their next update, or they’ll lose onion‑only access. Existing Tor data stays intact, but the switch isn’t automatic.
This extra step highlights the growing emphasis on censorship‑resistant payment routes in crypto commerce. It also reminds operators that privacy isn’t set‑and‑forget—it requires ongoing attention.
💬 How will you handle the opt‑in process for your BTCPay deployment? BTCPay Tor CryptoPrivacy
#BTCPay #Tor #CryptoPrivacy
26
·
--
#BitcoinCoreDisclosesTorTrafficVulnerability 🚨 BREAKING: Bitcoin Core Discloses Tor Traffic Vulnerability
This is HUGE for every Node Runner & Privacy user! 👇
What happened?
Bitcoin Core revealed CVE-2025-62860 - a Tor flaw that let ANY stranger on Tor get TRUSTED permissions on thousands of nodes! 😱
How?
➡️ Tor traffic was treated as LOCAL traffic
➡️ If node had -whitelist enabled, Tor strangers bypassed spam + privacy protections
➡️ Thousands of reachable mainnet nodes were whitelisting ALL incoming Tor connections
Good News:
✅ NO coins lost, NO wallets hacked
✅ Fixed in Oct 2025 in v30.0, v29.2, v28.3
✅ Nodes WITHOUT whitelist = NOT affected
✅ Disclosed Nov 10 after 29.x retired
BUT also disclosed:
⚠️ CVE-2025-62861 HIGH - Could stop mining nodes from making valid blocks
⚠️ CVE-2025-62859 MEDIUM - Could stall block processing 10 mins
What to do NOW?
1. Update to latest Bitcoin Core ASAP
2. Check your -whitelist settings
3. If you run a Tor node, VERIFY your config
Bitcoin is still secure - this is responsible disclosure working!
Are you running a node? 👇
🟢 = Already Updated
🟡 = Updating Now
🔴 = Didn't know
RT to warn every node runner!
#Bitcoin #BTC #Tor #BitcoinCore #CryptoSecurity #Binance
#BitcoinCoreDisclosesTorTrafficVulnerability 🚨 BREAKING: Bitcoin Core Discloses Tor Traffic Vulnerability
This is HUGE for every Node Runner & Privacy user! 👇
What happened?
Bitcoin Core revealed CVE-2025-62860 - a Tor flaw that let ANY stranger on Tor get TRUSTED permissions on thousands of nodes! 😱
How?
➡️ Tor traffic was treated as LOCAL traffic
➡️ If node had -whitelist enabled, Tor strangers bypassed spam + privacy protections
➡️ Thousands of reachable mainnet nodes were whitelisting ALL incoming Tor connections
Good News:
✅ NO coins lost, NO wallets hacked
✅ Fixed in Oct 2025 in v30.0, v29.2, v28.3
✅ Nodes WITHOUT whitelist = NOT affected
✅ Disclosed Nov 10 after 29.x retired
BUT also disclosed:
⚠️ CVE-2025-62861 HIGH - Could stop mining nodes from making valid blocks
⚠️ CVE-2025-62859 MEDIUM - Could stall block processing 10 mins
What to do NOW?
1. Update to latest Bitcoin Core ASAP
2. Check your -whitelist settings
3. If you run a Tor node, VERIFY your config
Bitcoin is still secure - this is responsible disclosure working!
Are you running a node? 👇
🟢 = Already Updated
🟡 = Updating Now
🔴 = Didn't know
RT to warn every node runner!
#Bitcoin #BTC #Tor #BitcoinCore #CryptoSecurity #Binance
This is HUGE for every Node Runner & Privacy user! 👇
What happened?
Bitcoin Core revealed CVE-2025-62860 - a Tor flaw that let ANY stranger on Tor get TRUSTED permissions on thousands of nodes! 😱
How?
➡️ Tor traffic was treated as LOCAL traffic
➡️ If node had -whitelist enabled, Tor strangers bypassed spam + privacy protections
➡️ Thousands of reachable mainnet nodes were whitelisting ALL incoming Tor connections
Good News:
✅ NO coins lost, NO wallets hacked
✅ Fixed in Oct 2025 in v30.0, v29.2, v28.3
✅ Nodes WITHOUT whitelist = NOT affected
✅ Disclosed Nov 10 after 29.x retired
BUT also disclosed:
⚠️ CVE-2025-62861 HIGH - Could stop mining nodes from making valid blocks
⚠️ CVE-2025-62859 MEDIUM - Could stall block processing 10 mins
What to do NOW?
1. Update to latest Bitcoin Core ASAP
2. Check your -whitelist settings
3. If you run a Tor node, VERIFY your config
Bitcoin is still secure - this is responsible disclosure working!
Are you running a node? 👇
🟢 = Already Updated
🟡 = Updating Now
🔴 = Didn't know
RT to warn every node runner!
#Bitcoin #BTC #Tor #BitcoinCore #CryptoSecurity #Binance
SHERAZ FAHEEM 01:
Security discussions are healthy for Bitcoin because they encourage stronger infrastructure and better development practices.
2
1
100
#BitcoinCoreDisclosesTorTrafficVulnerability
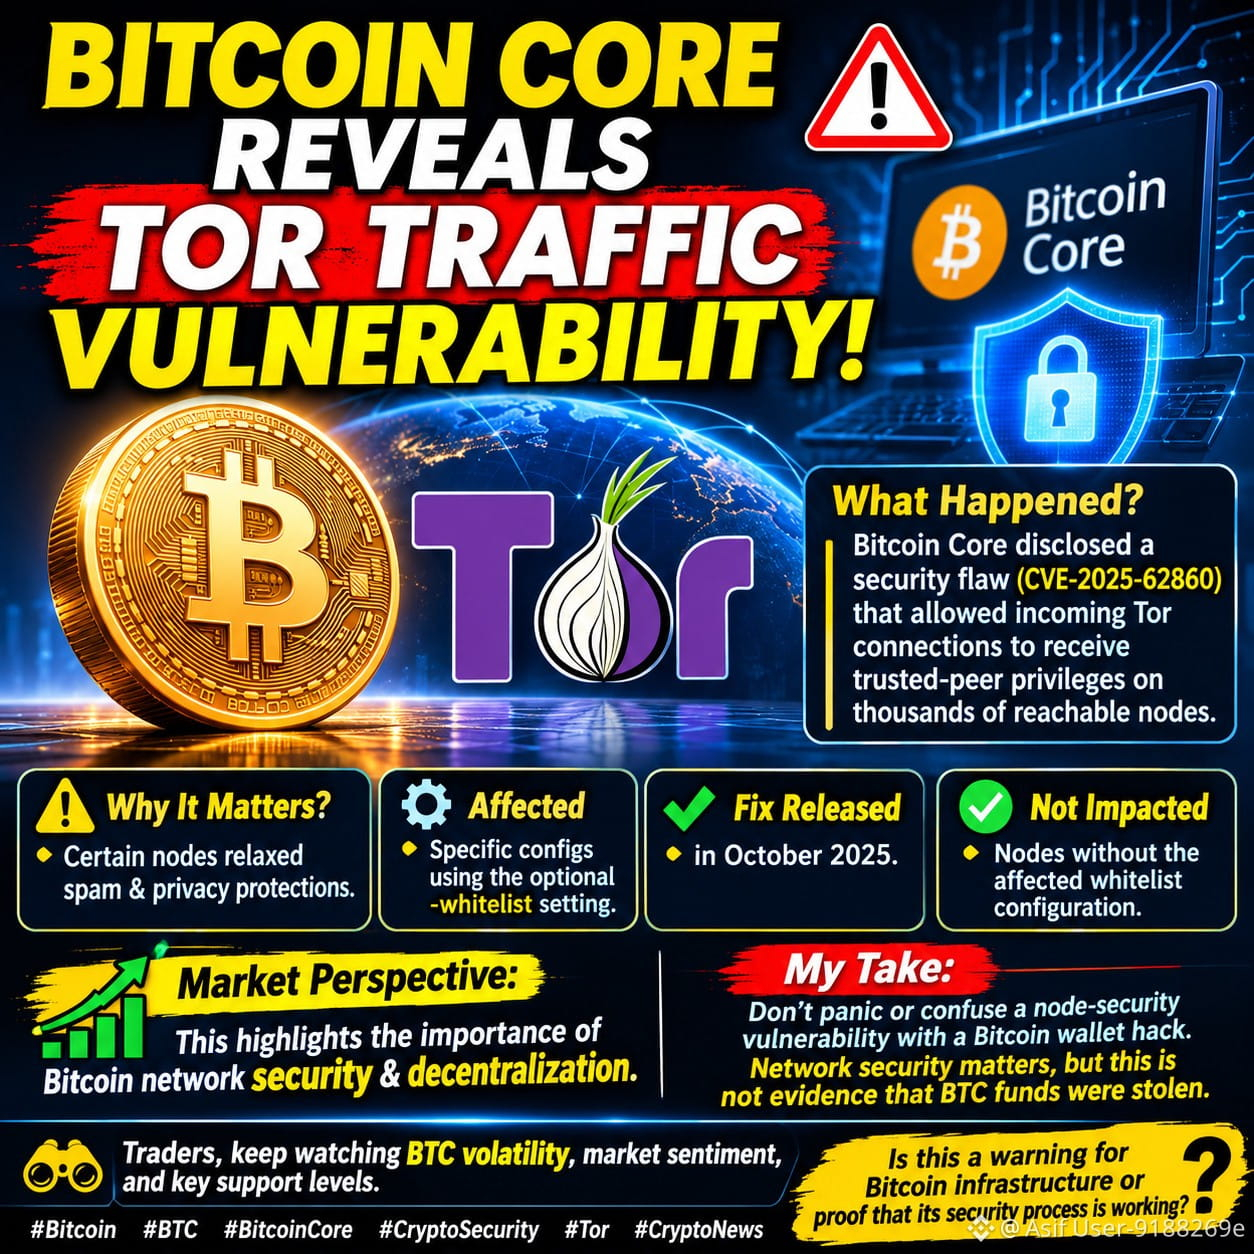
🚨 BITCOIN CORE REVEALS TOR TRAFFIC VULNERABILITY! 🔥
Bitcoin Core has disclosed a security flaw (CVE-2025-62860) that allowed incoming Tor connections to receive trusted-peer privileges on thousands of reachable Bitcoin nodes.
⚠️ Why does it matter?
Certain nodes unintentionally relaxed spam and privacy protections.
The issue affected specific configurations using the optional -whitelist setting.
Developers released fixes in October 2025.
Nodes without the affected whitelist configuration were not impacted.
📊 Market Perspective: This disclosure highlights the importance of Bitcoin network security, decentralization, and continuous upgrades.
My Take: Don't panic or confuse a node-security vulnerability with a Bitcoin wallet hack. Network security matters, but this is not evidence that BTC funds were stolen.
👀 Traders, keep watching $BTC volatility, market sentiment, and key support levels.
Is this a warning for Bitcoin infrastructure or proof that its security process is working?
#Bitcoin #BTC #BitcoinCore #CryptoSecurity #Tor #CryptoNewss
#BitcoinCoreDisclosesTorTrafficVulnerability
🚨 BITCOIN CORE REVEALS TOR TRAFFIC VULNERABILITY! 🔥
Bitcoin Core has disclosed a security flaw (CVE-2025-62860) that allowed incoming Tor connections to receive trusted-peer privileges on thousands of reachable Bitcoin nodes.
⚠️ Why does it matter?
Certain nodes unintentionally relaxed spam and privacy protections.
The issue affected specific configurations using the optional -whitelist setting.
Developers released fixes in October 2025.
Nodes without the affected whitelist configuration were not impacted.
📊 Market Perspective: This disclosure highlights the importance of Bitcoin network security, decentralization, and continuous upgrades.
My Take: Don't panic or confuse a node-security vulnerability with a Bitcoin wallet hack. Network security matters, but this is not evidence that BTC funds were stolen.
👀 Traders, keep watching $BTC volatility, market sentiment, and key support levels.
Is this a warning for Bitcoin infrastructure or proof that its security process is working?
#Bitcoin #BTC #BitcoinCore #CryptoSecurity #Tor #CryptoNewss
🚨 BITCOIN CORE REVEALS TOR TRAFFIC VULNERABILITY! 🔥
Bitcoin Core has disclosed a security flaw (CVE-2025-62860) that allowed incoming Tor connections to receive trusted-peer privileges on thousands of reachable Bitcoin nodes.
⚠️ Why does it matter?
Certain nodes unintentionally relaxed spam and privacy protections.
The issue affected specific configurations using the optional -whitelist setting.
Developers released fixes in October 2025.
Nodes without the affected whitelist configuration were not impacted.
📊 Market Perspective: This disclosure highlights the importance of Bitcoin network security, decentralization, and continuous upgrades.
My Take: Don't panic or confuse a node-security vulnerability with a Bitcoin wallet hack. Network security matters, but this is not evidence that BTC funds were stolen.
👀 Traders, keep watching $BTC volatility, market sentiment, and key support levels.
Is this a warning for Bitcoin infrastructure or proof that its security process is working?
#Bitcoin #BTC #BitcoinCore #CryptoSecurity #Tor #CryptoNewss
SHERAZ FAHEEM 01:
Bitcoin's long-term strength depends on developers continuously reviewing and improving its security model.
1
9
·
--
#BitcoinCoreDisclosesTorTrafficVulnerability
BITCOIN CORE JUST DISCLOSED A TOR VULNERABILITY. 🛡️⚠️
Your privacy layer had a crack.
Not your coins. Not your keys.
But your network traffic.
Bitcoin Core found it — and disclosed it.
That's what real decentralization looks like:
No hiding. No cover-up. Just transparency.
Are you still running your node on Tor?
Comment: SAFE 🟢 or WORRIED 🔴
#bitcoin #Tor #Privacy #BinanceSquare
#BitcoinCoreDisclosesTorTrafficVulnerability
BITCOIN CORE JUST DISCLOSED A TOR VULNERABILITY. 🛡️⚠️
Your privacy layer had a crack.
Not your coins. Not your keys.
But your network traffic.
Bitcoin Core found it — and disclosed it.
That's what real decentralization looks like:
No hiding. No cover-up. Just transparency.
Are you still running your node on Tor?
Comment: SAFE 🟢 or WORRIED 🔴
#bitcoin #Tor #Privacy #BinanceSquare
BITCOIN CORE JUST DISCLOSED A TOR VULNERABILITY. 🛡️⚠️
Your privacy layer had a crack.
Not your coins. Not your keys.
But your network traffic.
Bitcoin Core found it — and disclosed it.
That's what real decentralization looks like:
No hiding. No cover-up. Just transparency.
Are you still running your node on Tor?
Comment: SAFE 🟢 or WORRIED 🔴
#bitcoin #Tor #Privacy #BinanceSquare
1
211
·
--
#BitcoinCoreDisclosesTorTrafficVulnerability
🚨 Bitcoin Core just disclosed 3 bugs, and all of them were already fixed
The advisories went public Nov 10, but the fixes shipped in October 2025. Here's the breakdown: (theblock)
🔓 CVE-2025-62860 (medium): Tor peers could get whitelist permissions on nodes using the optional -whitelist setting. Bitcoin Core said "thousands" of reachable nodes were affected, which removed some DoS limits and privacy protections.
⛏️ CVE-2025-62861 (high): miners hit by it had to restart their nodes to create valid block templates again.
📦 CVE-2025-62859 (medium): a block-relay (compact block) issue. (theblock) (theblock)
Why the delay? Bitcoin Core ships the fix first and describes the bug later. The last vulnerable version went end of life on Oct. 27. (theblock)
What to do: Version 30.0 fixes all three. Version 29.2 carries the fixes too. If you run a plug-and-play node bundle with Tor, check whether it sets -whitelist. (theblock)
For traders: these are node-software issues that sit outside Bitcoin's consensus rules. It's an infrastructure story, not a protocol failure. (theunhashed)
🗣️ Do you run your own node or rely on an exchange? 👇
#BitcoinCore #CryptoSecurity #Bitcoin #Tor $BTC $ETH
Not financial advice.
#BitcoinCoreDisclosesTorTrafficVulnerability
🚨 Bitcoin Core just disclosed 3 bugs, and all of them were already fixed
The advisories went public Nov 10, but the fixes shipped in October 2025. Here's the breakdown: (theblock)
🔓 CVE-2025-62860 (medium): Tor peers could get whitelist permissions on nodes using the optional -whitelist setting. Bitcoin Core said "thousands" of reachable nodes were affected, which removed some DoS limits and privacy protections.
⛏️ CVE-2025-62861 (high): miners hit by it had to restart their nodes to create valid block templates again.
📦 CVE-2025-62859 (medium): a block-relay (compact block) issue. (theblock) (theblock)
Why the delay? Bitcoin Core ships the fix first and describes the bug later. The last vulnerable version went end of life on Oct. 27. (theblock)
What to do: Version 30.0 fixes all three. Version 29.2 carries the fixes too. If you run a plug-and-play node bundle with Tor, check whether it sets -whitelist. (theblock)
For traders: these are node-software issues that sit outside Bitcoin's consensus rules. It's an infrastructure story, not a protocol failure. (theunhashed)
🗣️ Do you run your own node or rely on an exchange? 👇
#BitcoinCore #CryptoSecurity #Bitcoin #Tor $BTC $ETH
Not financial advice.
🚨 Bitcoin Core just disclosed 3 bugs, and all of them were already fixed
The advisories went public Nov 10, but the fixes shipped in October 2025. Here's the breakdown: (theblock)
🔓 CVE-2025-62860 (medium): Tor peers could get whitelist permissions on nodes using the optional -whitelist setting. Bitcoin Core said "thousands" of reachable nodes were affected, which removed some DoS limits and privacy protections.
⛏️ CVE-2025-62861 (high): miners hit by it had to restart their nodes to create valid block templates again.
📦 CVE-2025-62859 (medium): a block-relay (compact block) issue. (theblock) (theblock)
Why the delay? Bitcoin Core ships the fix first and describes the bug later. The last vulnerable version went end of life on Oct. 27. (theblock)
What to do: Version 30.0 fixes all three. Version 29.2 carries the fixes too. If you run a plug-and-play node bundle with Tor, check whether it sets -whitelist. (theblock)
For traders: these are node-software issues that sit outside Bitcoin's consensus rules. It's an infrastructure story, not a protocol failure. (theunhashed)
🗣️ Do you run your own node or rely on an exchange? 👇
#BitcoinCore #CryptoSecurity #Bitcoin #Tor $BTC $ETH
Not financial advice.
1
43
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#WhoWillSucceedJensenHuangatNvidia?
81,433 views
1,099 Discussing
2
#WhatWillDriveCryptoandStocks’NextRebound?
431,655 views
3,003 Discussing
3
#BitcoinActiveSupplyInProfitDropsBelow45%
21,738 views
326 Discussing
4
#KavaSaysAbnormalActivityLimitedToKavaLend
8,507 views
163 Discussing
5
#USSpotXRPETFsSeeLargestWeeklyOutflowIn8Months
7,720 views
155 Discussing
6
#USPPIMissMayEaseBTCPressure
206,752 views
2,036 Discussing
7
#WORPTLetsTouristsConvertCryptoToThaiBaht
2,550 views
49 Discussing
8
#TONStrategyReports$23.97MQ3NetLoss
3,193 views
41 Discussing
9
#PolkadotCommunityApprovesNewStrategyWith97%Vote
18,626 views
241 Discussing
10
#dYdXPlansV9.9UpgradeToShiftUSDCToInjective
11,380 views
193 Discussing